A few thingsabout me
haadi@portfolio:~$ cat -n whoami.txt
- Hi, I'm Haadi, a computer science student focused on blue-team security.
- My entry point is SOC analysis: threat detection, log analysis and SIEM engineering.
- I care about what happens after an alert fires, and what's missing before it.
- Every project here is real lab work: deployed, broken and fixed.
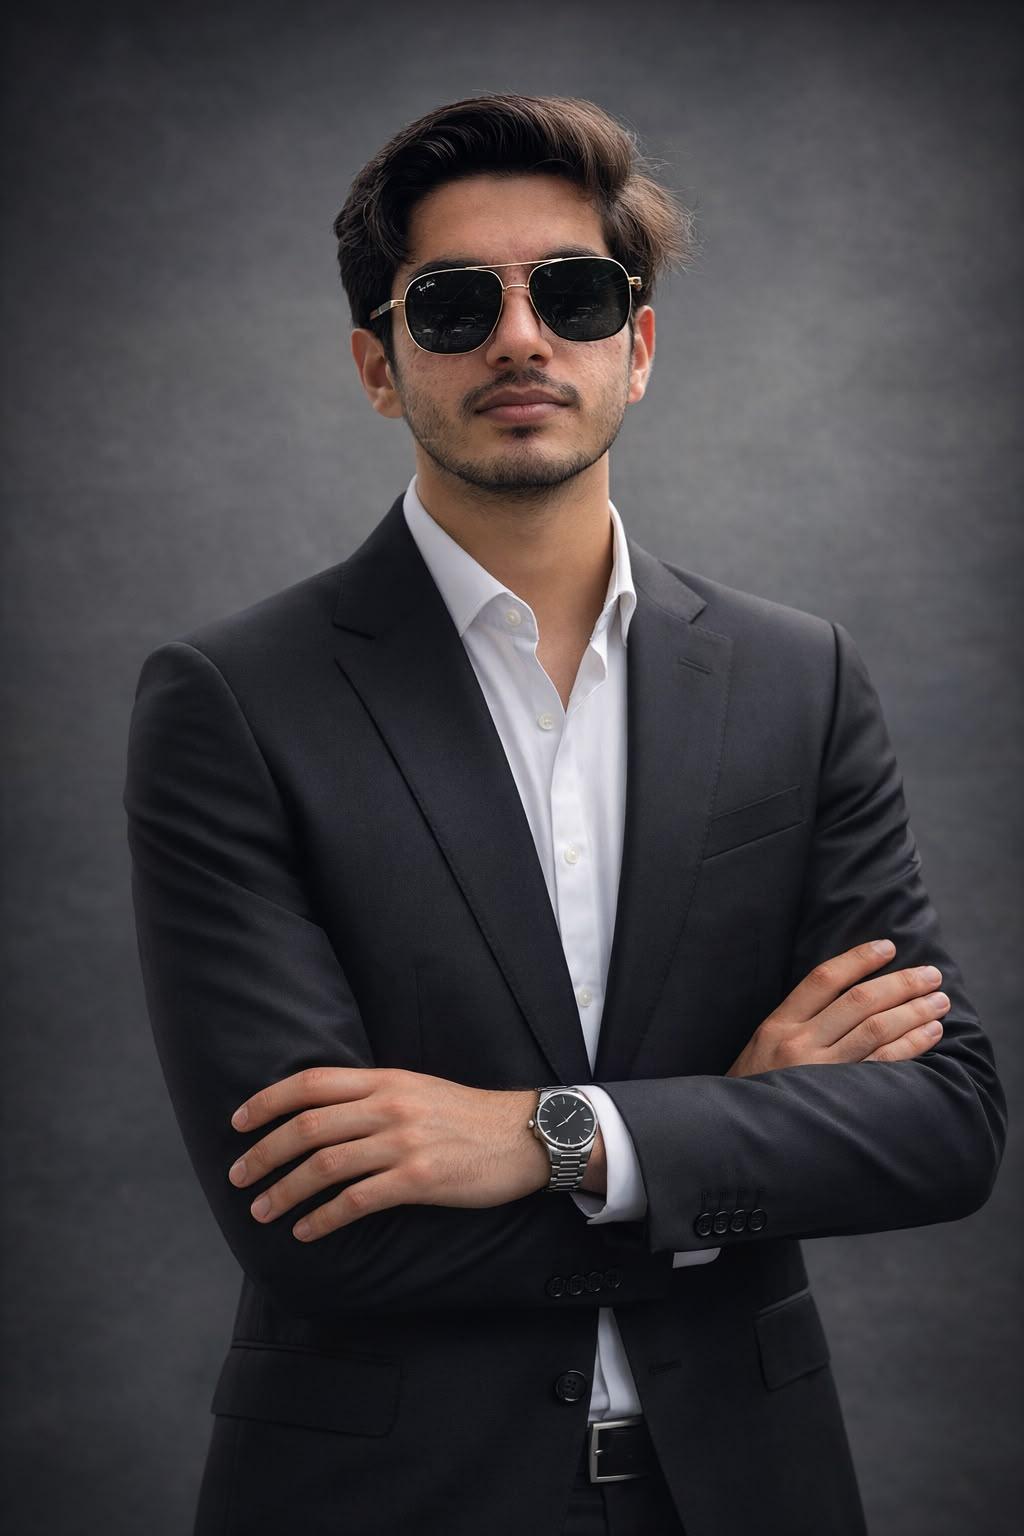
haadi@portfolio:~$ eog portrait.jpg
haadi@portfolio:~$ cat -n focus.txt
- Detection engineering: Wazuh, MITRE ATT&CK, Snort
- SOC automation: Shuffle, Webhooks, Splunk
- Security testing (lab): Nmap, Burp Suite, Metasploit
- Systems & software: C++, Python, SQL
Selectedprojects
Notes fromthe field
- 2026.07.22Security researchDetection engineering
Detecting Linux privilege escalation with custom Wazuh rules
Three rules for sudo abuse the default ruleset doesn't cover, how each was tuned against false positives, tested against a real simulated attack, and mapped to ATT&CK.
Wazuh · MITRE ATT&CK
- 2026.07.22Security researchDetection engineering
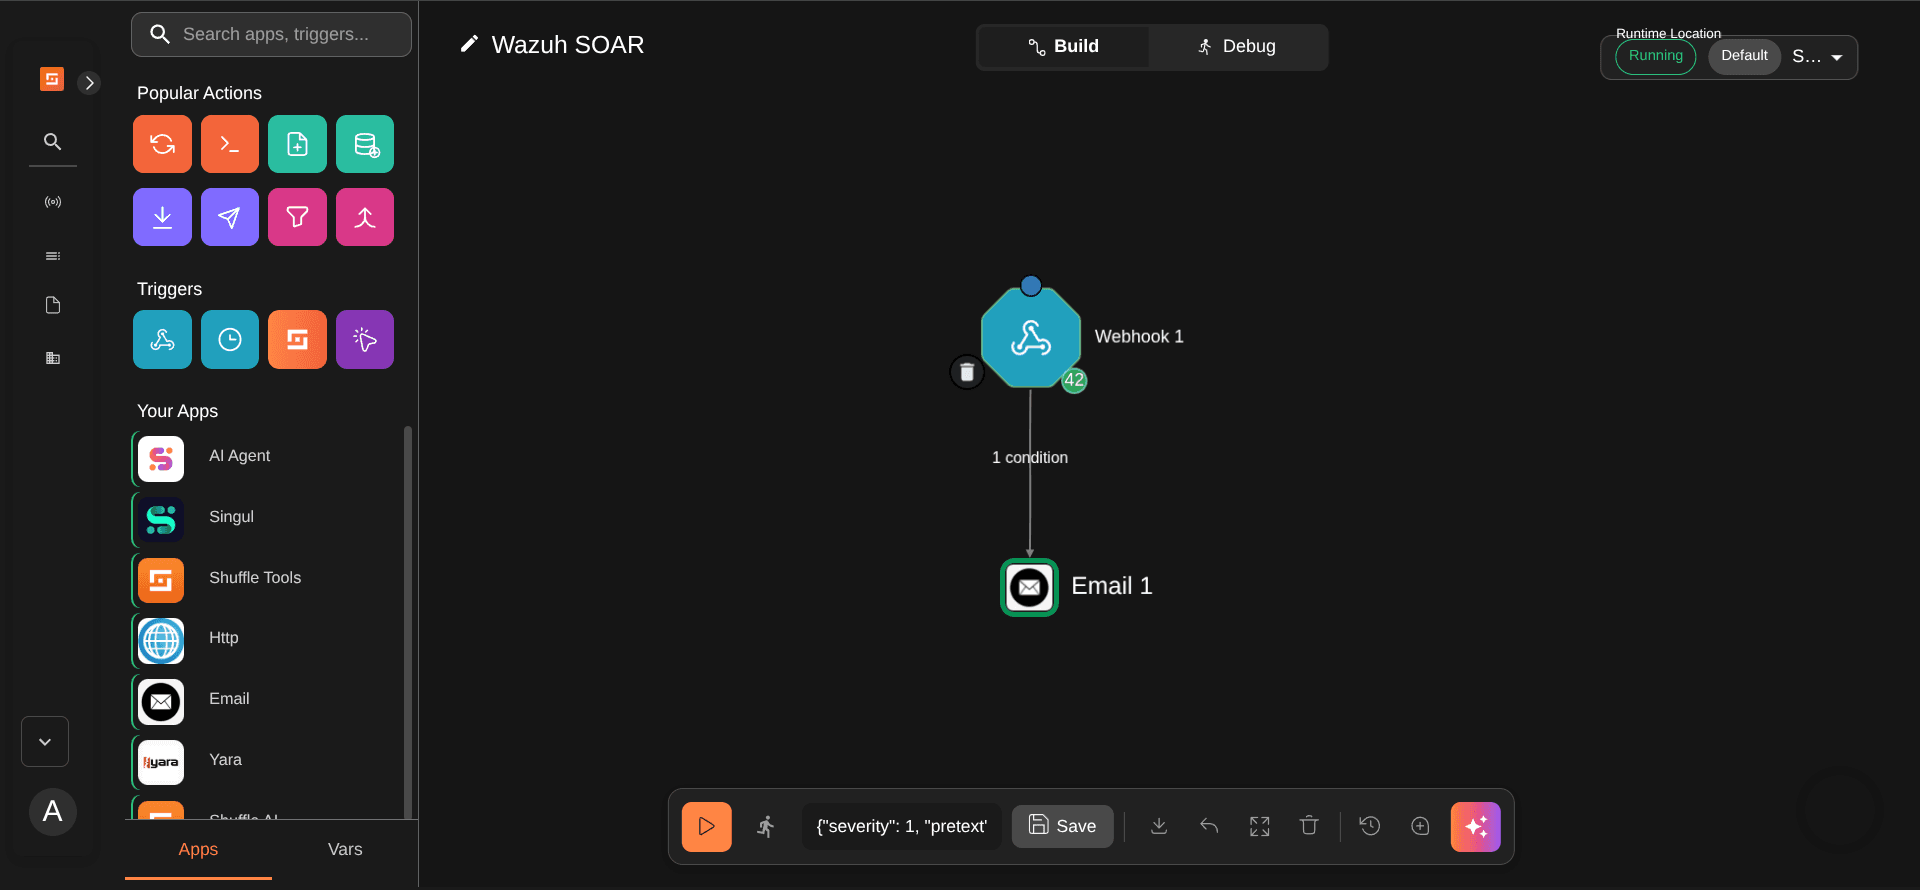
Wazuh → Shuffle SOAR Automation
A Shuffle workflow that receives Wazuh alerts over a webhook, filters them by severity, and automatically sends an email notification for anything serious enough to warrant one: instead of relying on someone watching the Wazuh dashboard.
Wazuh · Shuffle SOAR
- 2026.07.20Security researchDetection engineering
Automating Wazuh Alert Notifications Using Shuffle SOAR
A hands-on SIEM and SOAR integration lab: Wazuh detects a real SSH attack, forwards the alert to Shuffle, and an automated email notification fires within seconds: no manual dashboard monitoring required.
Wazuh · Shuffle SOAR
Let's work together on something secure
Open to SOC & security internships in Pakistan & remote. Internships, lab collaborations or a question about a write-up. I reply to every message.